SUPREMA
- PRODUITS
- Plateforme de sécurité
- BioStar X | Sécurité On-Premise
- BioStar Air | Sécurité cloud
- BioStar 2
- Contrôle d'accès
- Unité de contrôle d'accès
- Lecteur biométriqueNEW
- Lecteur RFID
- Badge mobile
- Périphériques
- Serrures Sans Fil
- SOLUTIONS
- ASSISTANCE
- À PROPOS


- Actualités
- Derniers communiqués de presse de Suprema


While digital Zero Trust network architectures are standard across modern data centers, a critical execution gap remains at the physical security end. Presenting a physical credential, whether a card badge, fob, or PIN, proves only that an object reached a reader, failing to verify who presented it. To achieve complete security alignment across physical and digital domains, data center access control solutions must institute an identity-first mandate where every access request is continuously bound to a verified individual.
Key Strategic Takeaways for Evaluating Security Stacks
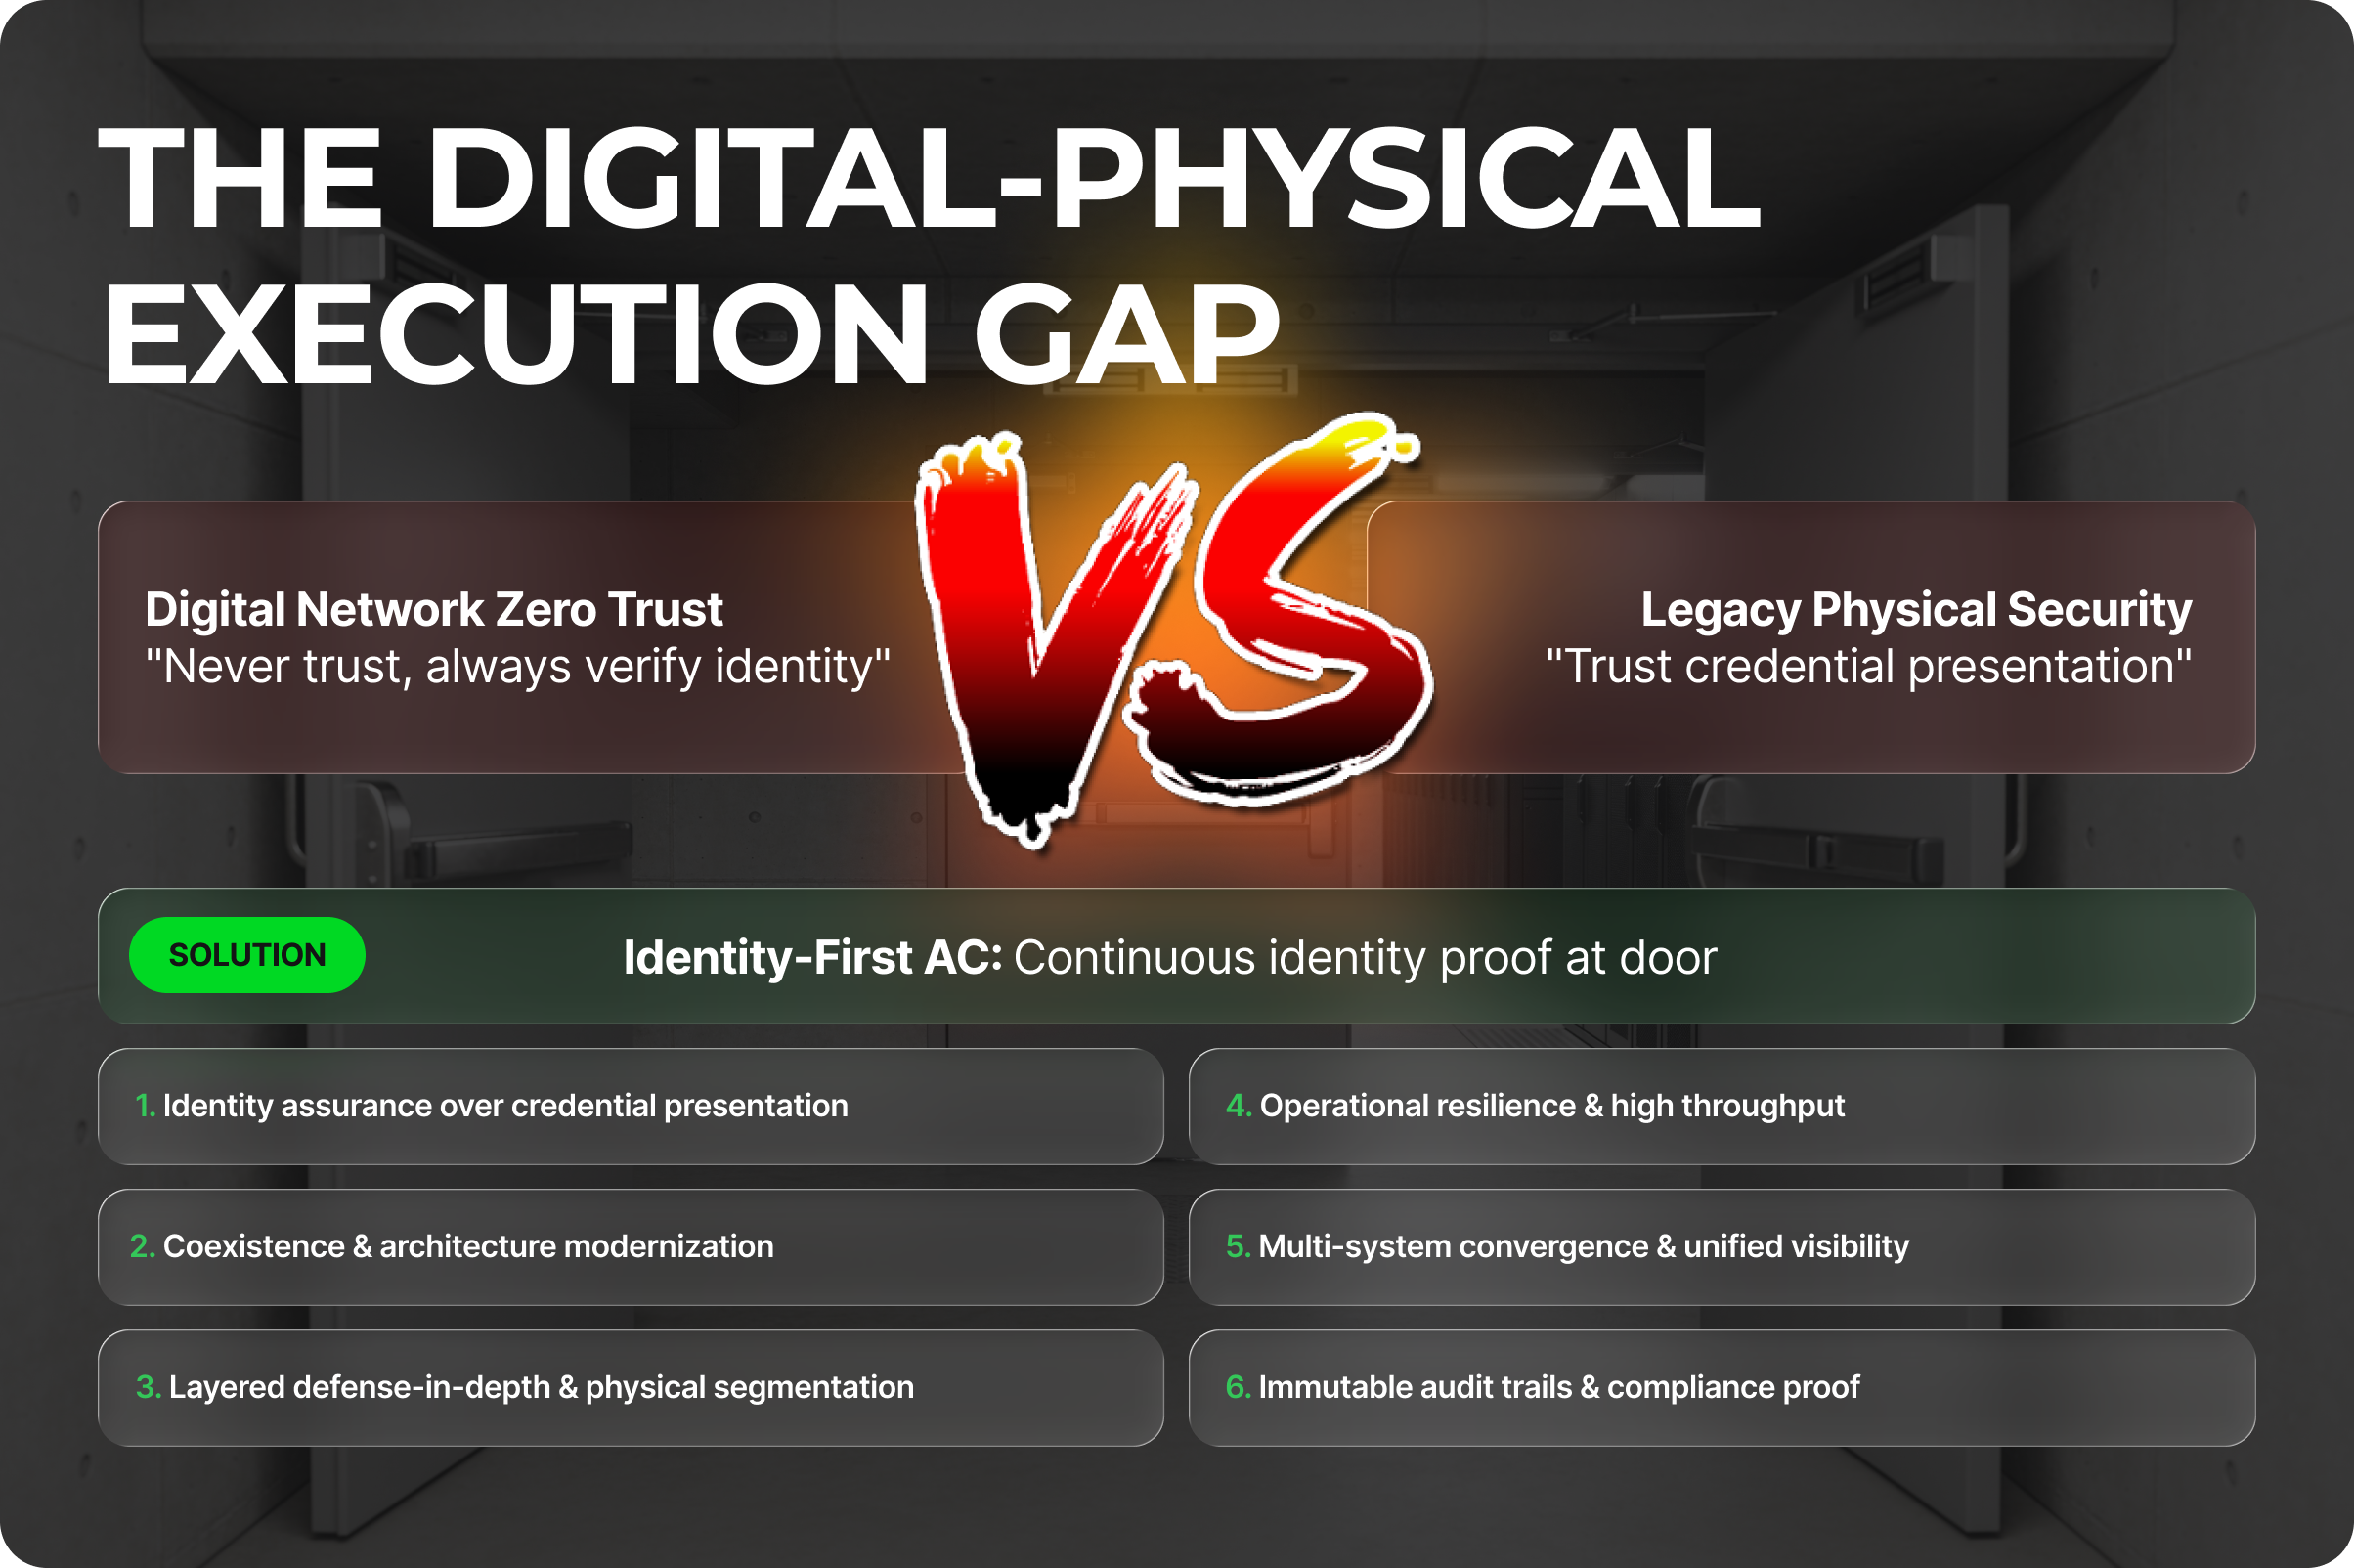
When evaluating physical access control solutions or building an end-to-end security architecture, data center operators should ground their criteria in six core pillars:
- Uncompromising Identity Verification: Go beyond simple credential checks by enforcing continuous multi-factor authentication (MFA) and AI-driven biometrics to bind physical access strictly to a confirmed individual.
- Architecture Modernization & Coexistence: Upgrade endpoint identity assurance without discarding legacy infrastructure by deploying intelligent controllers that interface seamlessly across OSDP and Wiegand protocols.
- Granular Physical & Access Segmentation: Eliminate lateral movement across the facility through layered defense-in-depth zones and access policies such as APB and single person access, extending from the outer perimeter down to individual server rack handles.
- Operational Resilience & High Throughput: Ensure high-speed biometric matching and environmental durability so strict physical security does not choke daily operational workflows or shift changes.
- Unified Domain Visibility: Eradicate monitoring silos by bringing access control, surveillance feeds, and IT identity providers under a single operational view, connected to an identity.
- Audit-Ready Continuous Compliance: Automatically generate immutable, encrypted access logs to meet stringent global regulatory standards like ISO 27001, SOC 2, and GDPR.
Why Is Credential-Based Access Control Failing Data Center Zero Trust Mandates?
Data center operators have invested heavily in digital Zero Trust frameworks, enforcing strict context, continuous authentication, and least-privilege policies across software networks. However, a major architectural disconnect persists: the execution gap between physical security and digital identity.
Traditional physical access control relies heavily on credential presentation. Presenting a physical badge, key fob, or standard RFID card merely proves that the object reached the reader; it fails to prove who presented it. Card cloning, badge sharing, lost credentials, and tailgating leave physical perimeters vulnerable, completely undermining digital Zero Trust principles.
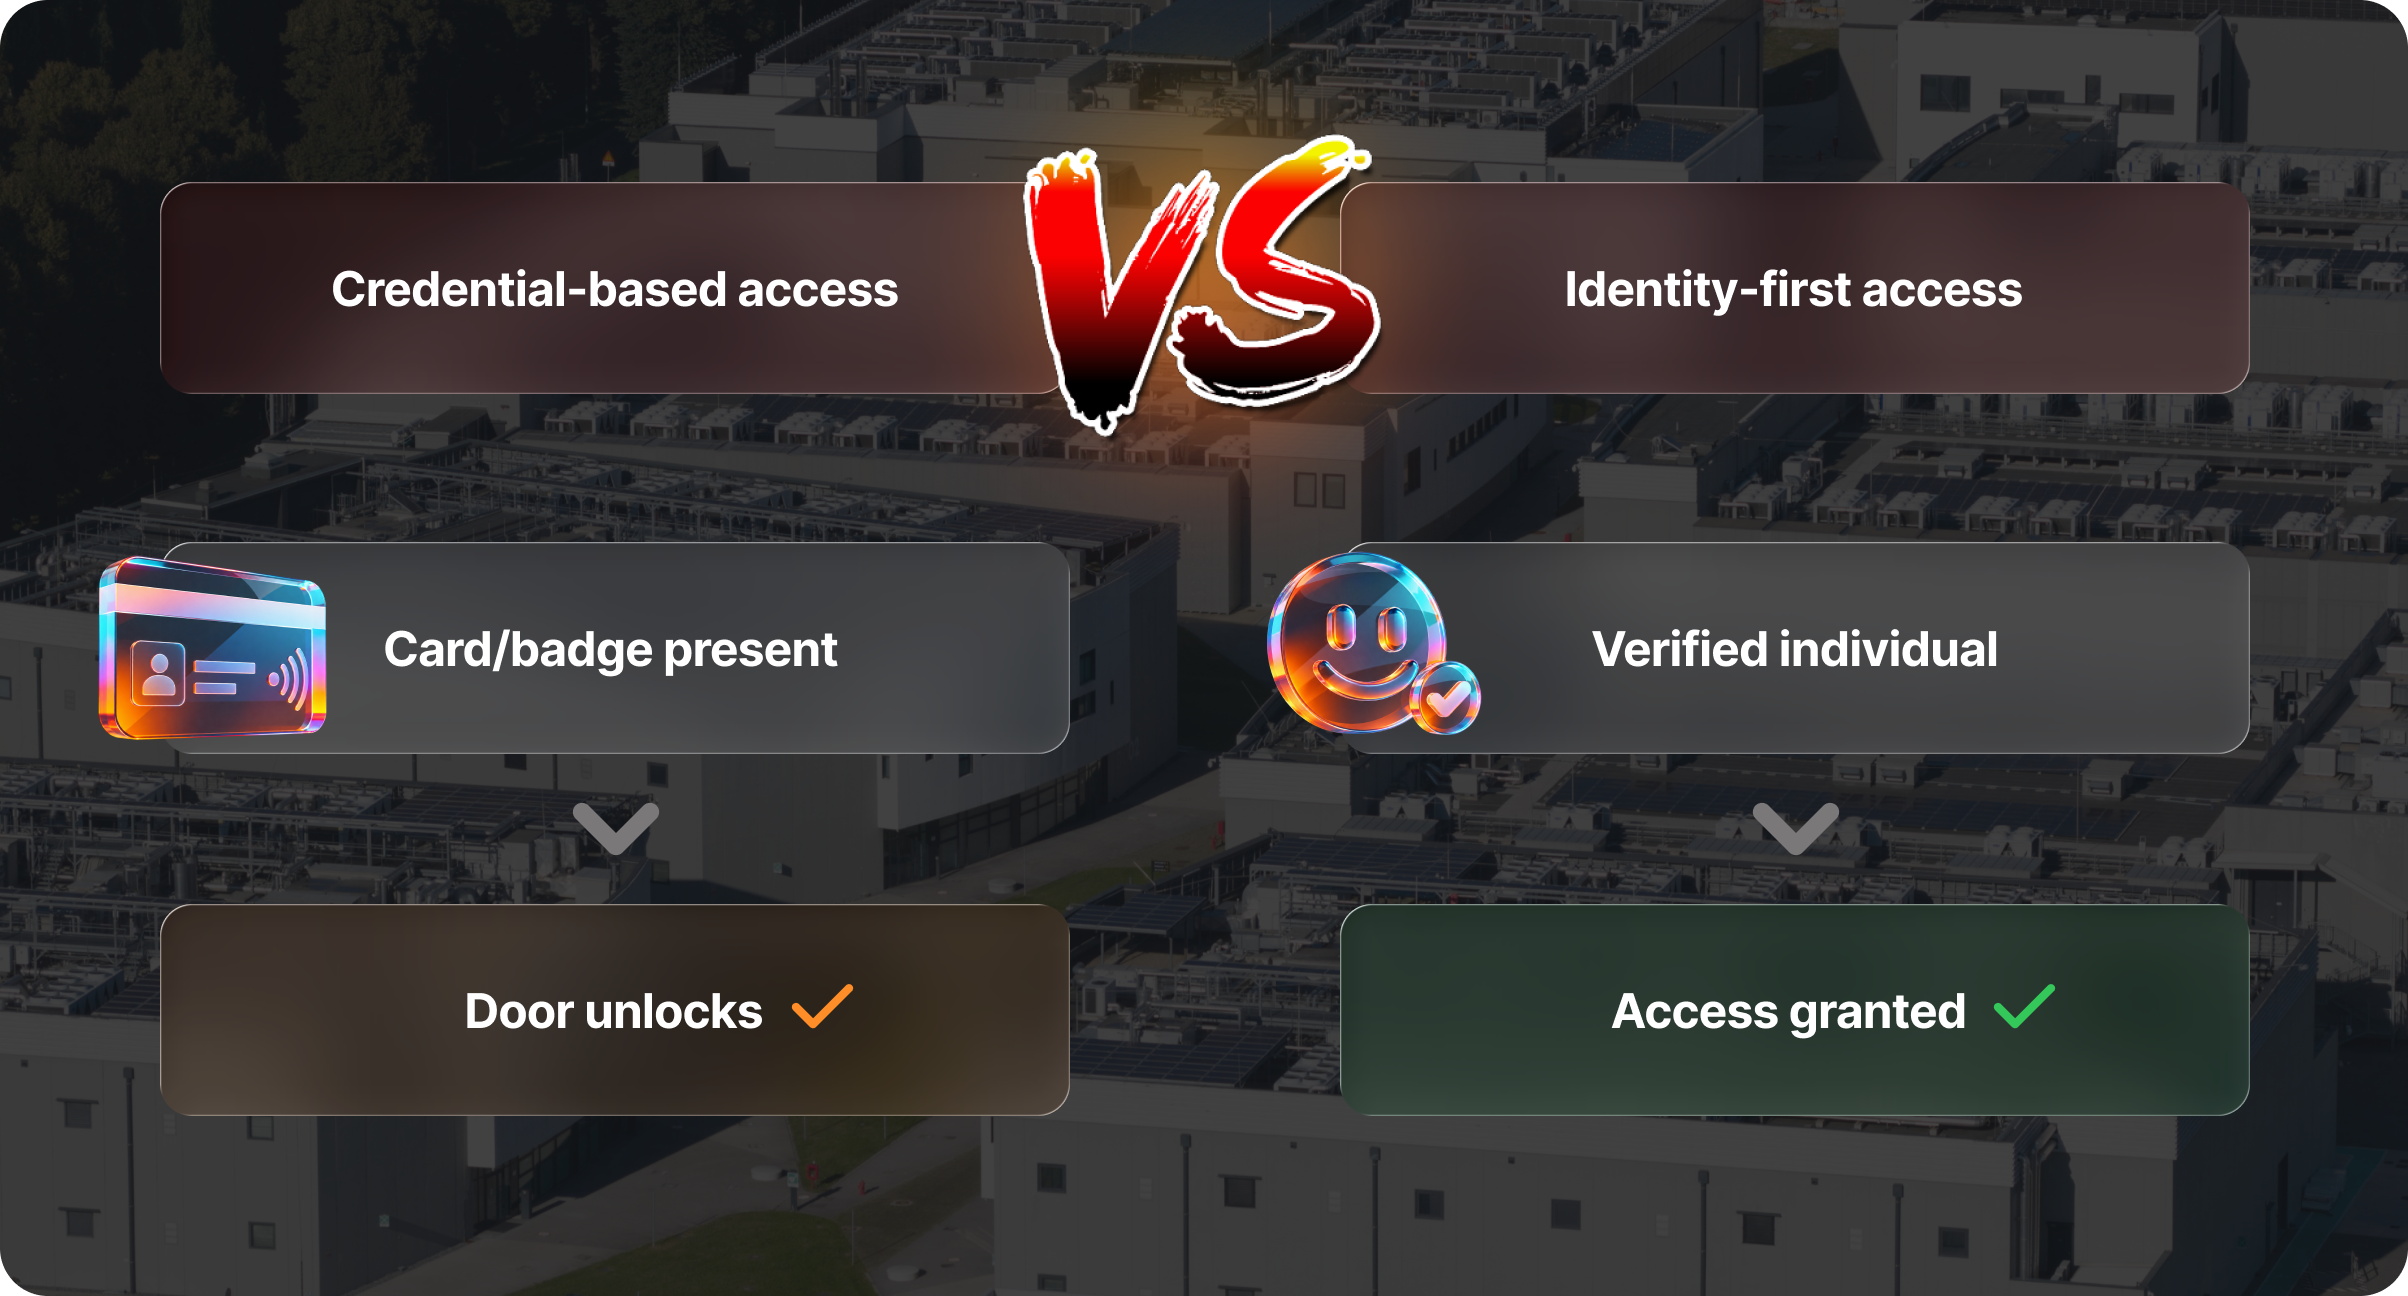
To achieve complete data center security, access cannot stop at credential validation. Facilities must enforce an identity-first mandate. Every physical interaction must bind directly to a verified identity, creating a seamless, connected chain of trust across both physical doors and digital servers.
What Are the 6 Strategic Pillars for Evaluating an Identity-First Security Stack?
When evaluating new access solutions or designing a physical security stack, data center security leaders should measure technologies against 6 core criteria:
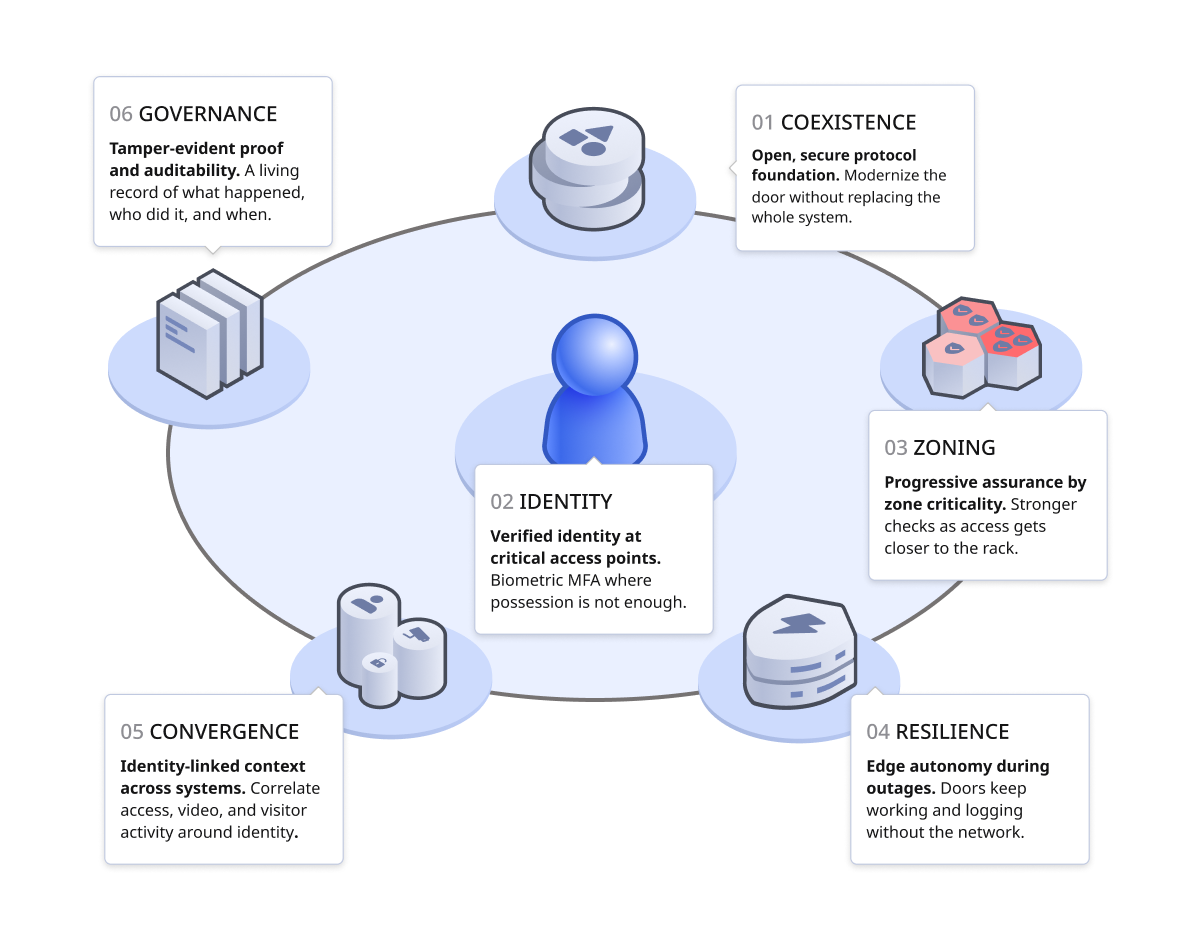
1. Identity Assurance Over Credential Presentation
Credentials can be shared, lost, or stolen. An identity-first architecture replaces simple badge checks with continuous multi-factor identity verification. By incorporating multi-factor biometrics, such as high-speed AI facial authentication combined with optical fingerprint sensing, access control systems guarantee that permissions are granted exclusively to the specific, verified individual.
2. Coexistence & Architecture Modernization
Transitioning to identity-first physical security should not require a costly "rip-and-replace" of existing infrastructure. Modern physical access control systems must support coexistence: integrating intelligent controllers that bridge advanced biometric readers with legacy panel hardware over standardized protocols like RS-485 (OSDP v2) or Wiegand. This allows facilities to modernize identity verification at the endpoint while preserving existing cabling investments.
3. Layered Defense-in-Depth & Physical Segmentation
Zero Trust dictates that physical spaces must be micro-segmented to restrict lateral movement. Facilities should enforce identity verification across 5 distinct physical layers:
- Perimeter Fence & Gate: Outer boundary verification for personnel and vehicles.
- Facility Main Entrance: High-throughput entry checks built for high traffic.
- Technical & Utility Zones: Restricted operational areas governed by intelligent controllers.
- Server Vault Rooms: High-security access points requiring multi-factor biometric checks.
- Cabinet & Server Racks: Precision identity locks applied directly at individual rack doors.
4. Operational Resilience & High Throughput
Strict identity verification must never compromise operational efficiency or cause entry delays. Biometric endpoints and access controllers must execute ultra-fast matching speeds to handle shift changes smoothly and authenticate access even during power outages or network disruptions, while ruggedized outdoor hardware maintains performance through harsh weather and high-stress environments.
5. Multi-System Convergence & Unified Visibility
Siloed systems create operational blind spots. A modern identity-first stack unifies physical access control, surveillance feeds, visitor logs, and intrusion alarms into a single management interface. Connecting physical security controls with IT identity providers (such as Active Directory) ensures real-time identity synchronization across all physical and digital domains.
6. Immutable Audit Trails & Compliance Proof
To satisfy stringent standards like ISO 27001, SOC 2 Type II, TIA-942, and GDPR, security teams must deliver unalterable access logs. Unified security software must automatically track, log, and encrypt every access attempt, configuration change, and administrative update to provide full audit readiness.
Which Technology Stack Delivers End-to-End Identity Unification?
Building an integrated physical Zero Trust architecture requires high-performance hardware and centralized control software.
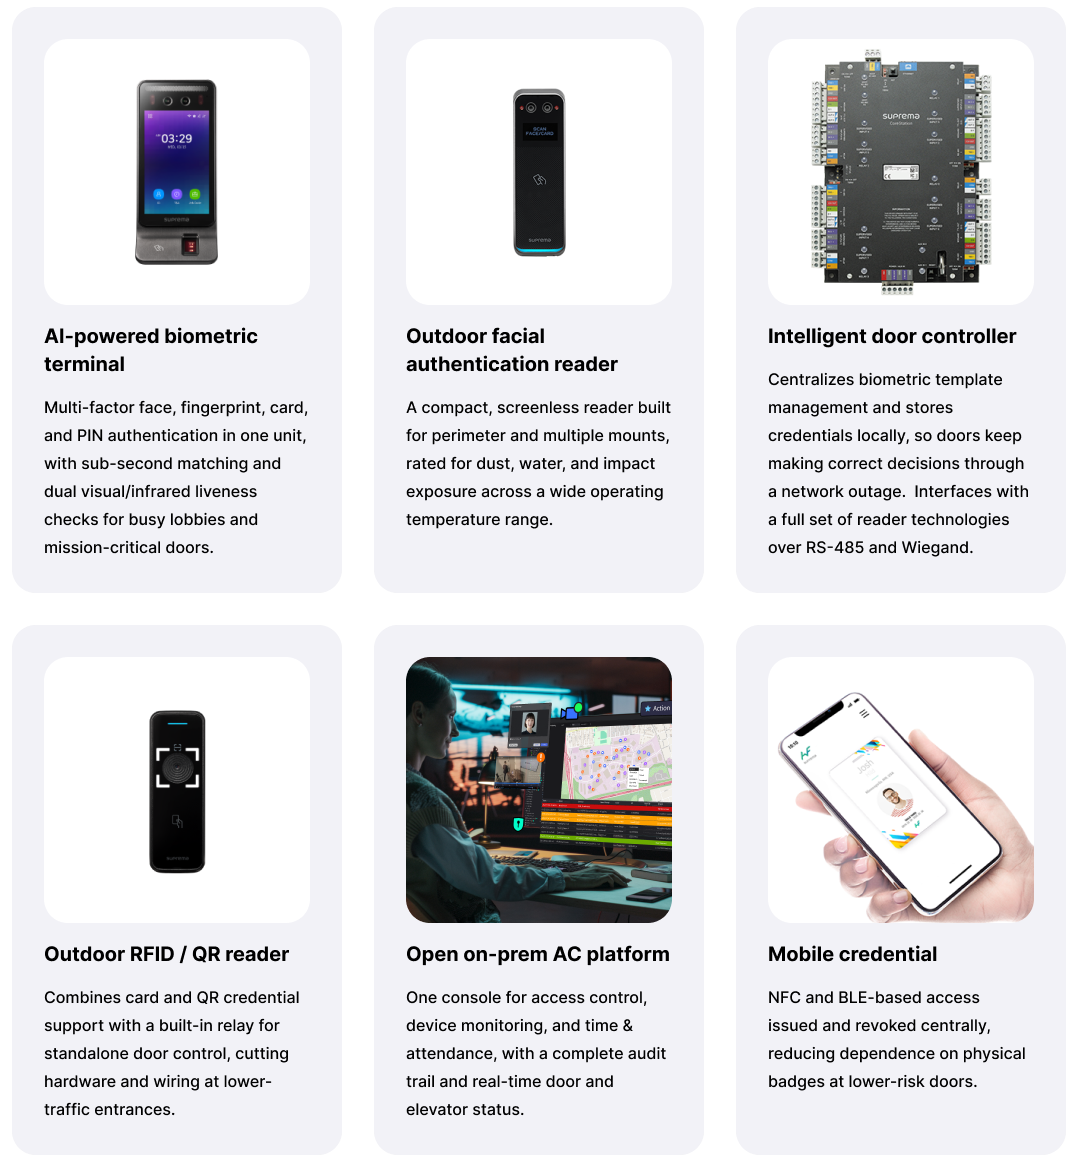
High-Assurance AI Biometric Endpoints
For internal server vaults and sensitive control rooms, the BioStation 3 Max delivers enterprise-grade identity assurance. Powered by an NPU platform, it provides fast AI facial authentication along with multi-factor authentication options including optical fingerprint sensing, RFID, mobile passes, QR codes, and PIN. Equipped with CC EAL6+ certified hardware components, Secure Boot, and a hardened OS, it ensures rapid processing while protecting biometric data.
For perimeter gates and exterior entrances, the BioEntry W3 provides AI facial authentication in a compact, screenless form factor. Featuring IP67 water/dust ingress protection and IK08 impact resistance, it maintains identity verification in rugged environment conditions.
Flexible Visitor Access Management
Managing contractor and visitor credentials without sacrificing security requires versatile endpoints. The XPass Q2 is a camera-based QR and RFID reader that supports dynamic QR codes, mobile credentials (NFC/BLE), and smart cards. Designed with PoE capability and an IP65 housing, it enables streamlined temporary access while keeping visitors bound to verified profiles.
Centralized Processing & Coexistence Controllers
To prevent storing biometric data on edge devices, the CoreStation intelligent controller centralizes matching logic and access decisions. Supporting multiple communication protocols (OSDP v2 and Wiegand), CoreStation allows data centers to deploy advanced biometric authentication on top of existing access control infrastructure.
On-prem Access Control Platform Natively Built Around Biometrics
Serving as the single point of access management, the BioStar X on-prem Access Control Platform consolidates access tracking, video streams, and alarm monitoring into one unified view. Featuring TLS 1.3 encryption on major communications channels, granular access rights, and real-time event logging, BioStar X provides complete system transparency and compliance reporting.
How to Begin Your Data Center Security Stack Upgrade
Moving from a traditional credential-based setup to a connected, identity-first physical Zero Trust architecture involves five key execution steps:
- Conduct a Credential Gap Audit: Assess where credential presentation (fobs/badges) currently exists without secondary identity verification.
- Establish Physical Layer Segmentation: Define clear security boundaries spanning perimeter gates down to server cabinet handles.
- Deploy Coexistence Architecture: Modernize access points with intelligent controllers like CoreStation to connect legacy hardware to biometric security.
- Implement High-Assurance Endpoints: Install edge AI access control devices like BioStation 3 Max at server room access points for multi-factor authentication.
- Centralize Management & Auditing: Integrate all physical devices into the BioStar X on-prem security platform for live operational monitoring and audit trail generation.
Ready to close the execution gap in your facility and evaluate your physical security stack against modern identity standards?
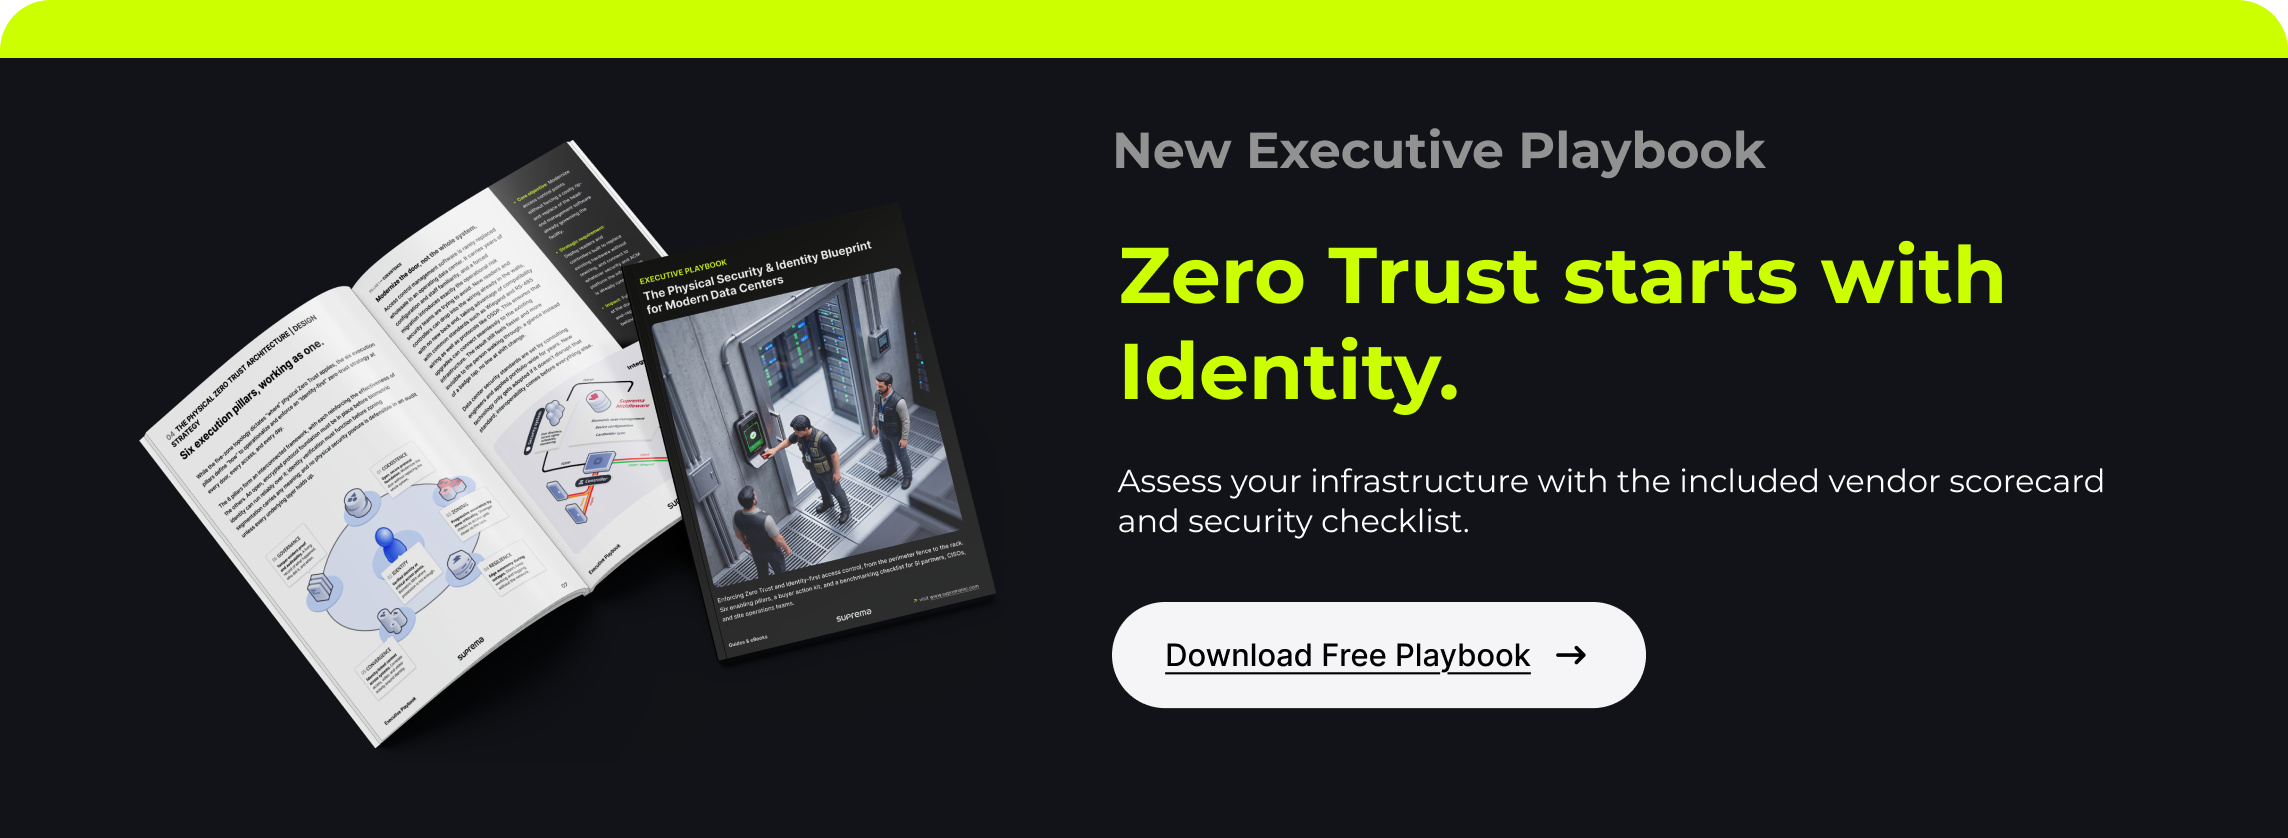
Download the Physical Zero-Trust Playbook for Data Centers >> to get 5-layer architectural diagrams, technology evaluation checklists, and complete vendor scorecards.


Merci.
Votre demande a bien été envoyée.
Nous vous répondrons sous peu.
Votre e-mail : partner@gmail.com
